Azure AD (Entra)
This page gives the steps to configure Azure AD as the Identity service provider for NocoDB.
NocoDB, Retrieve Redirect URL
- Go to
Account Settings. - Select
Authentication (SSO). - Click the
New Providerbutton. A popup modal opens. - In the popup modal, specify a
Display namefor the provider. The login page shows the provider with this name. - Copy the
Redirect URL. You configure it later in the Identity Provider.
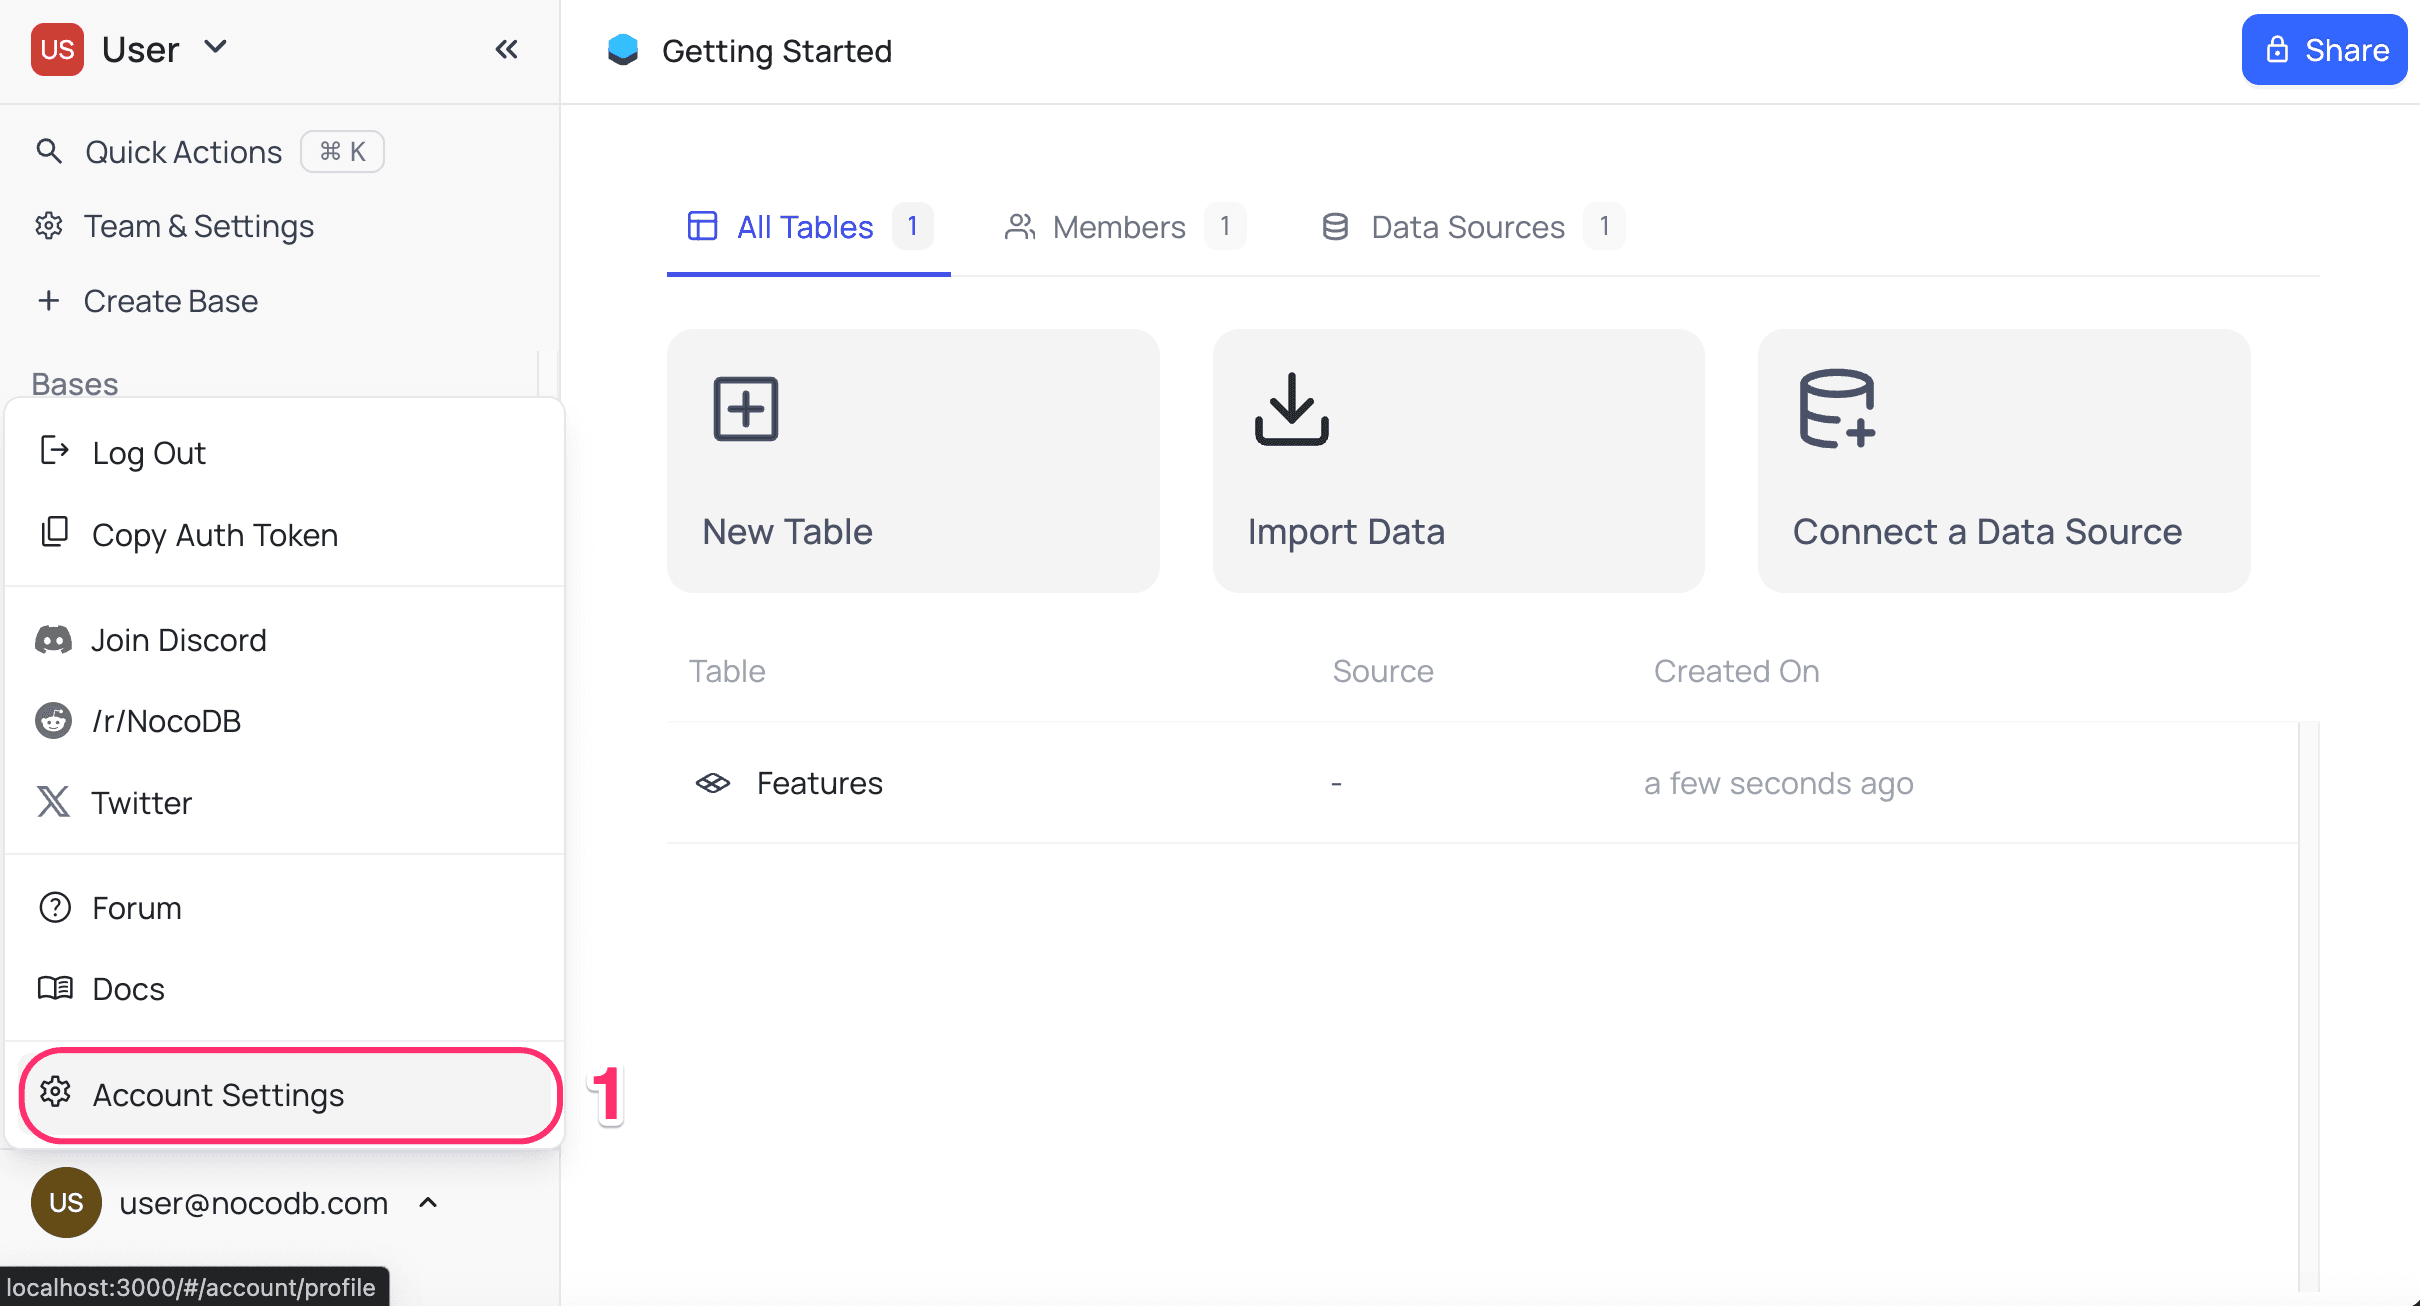
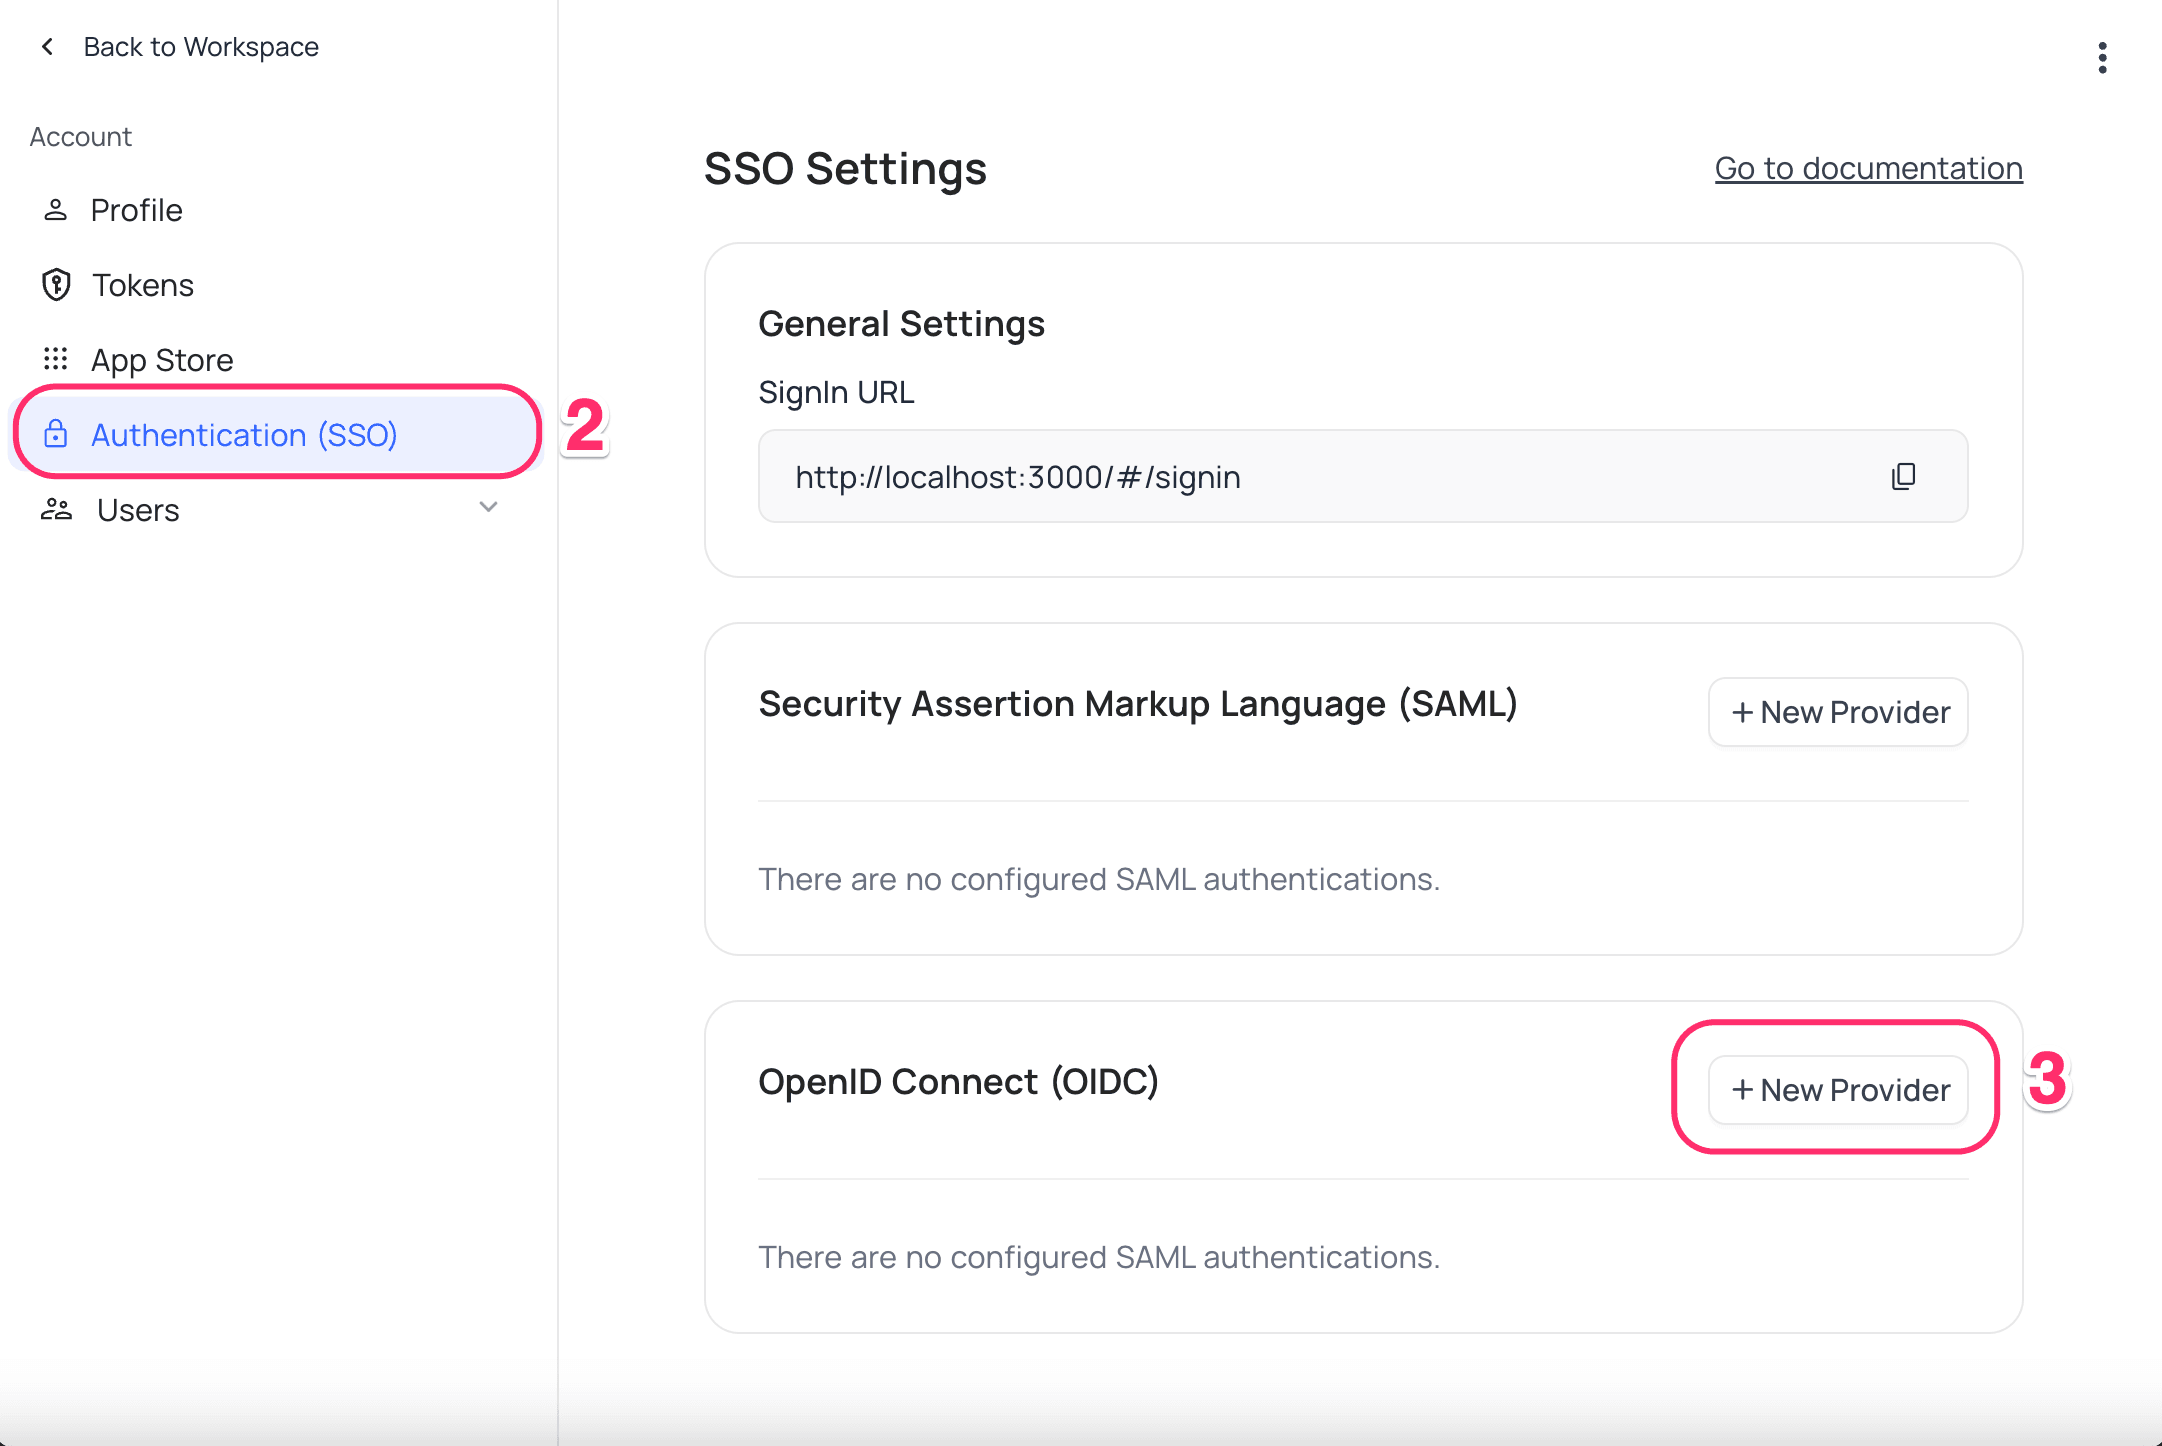
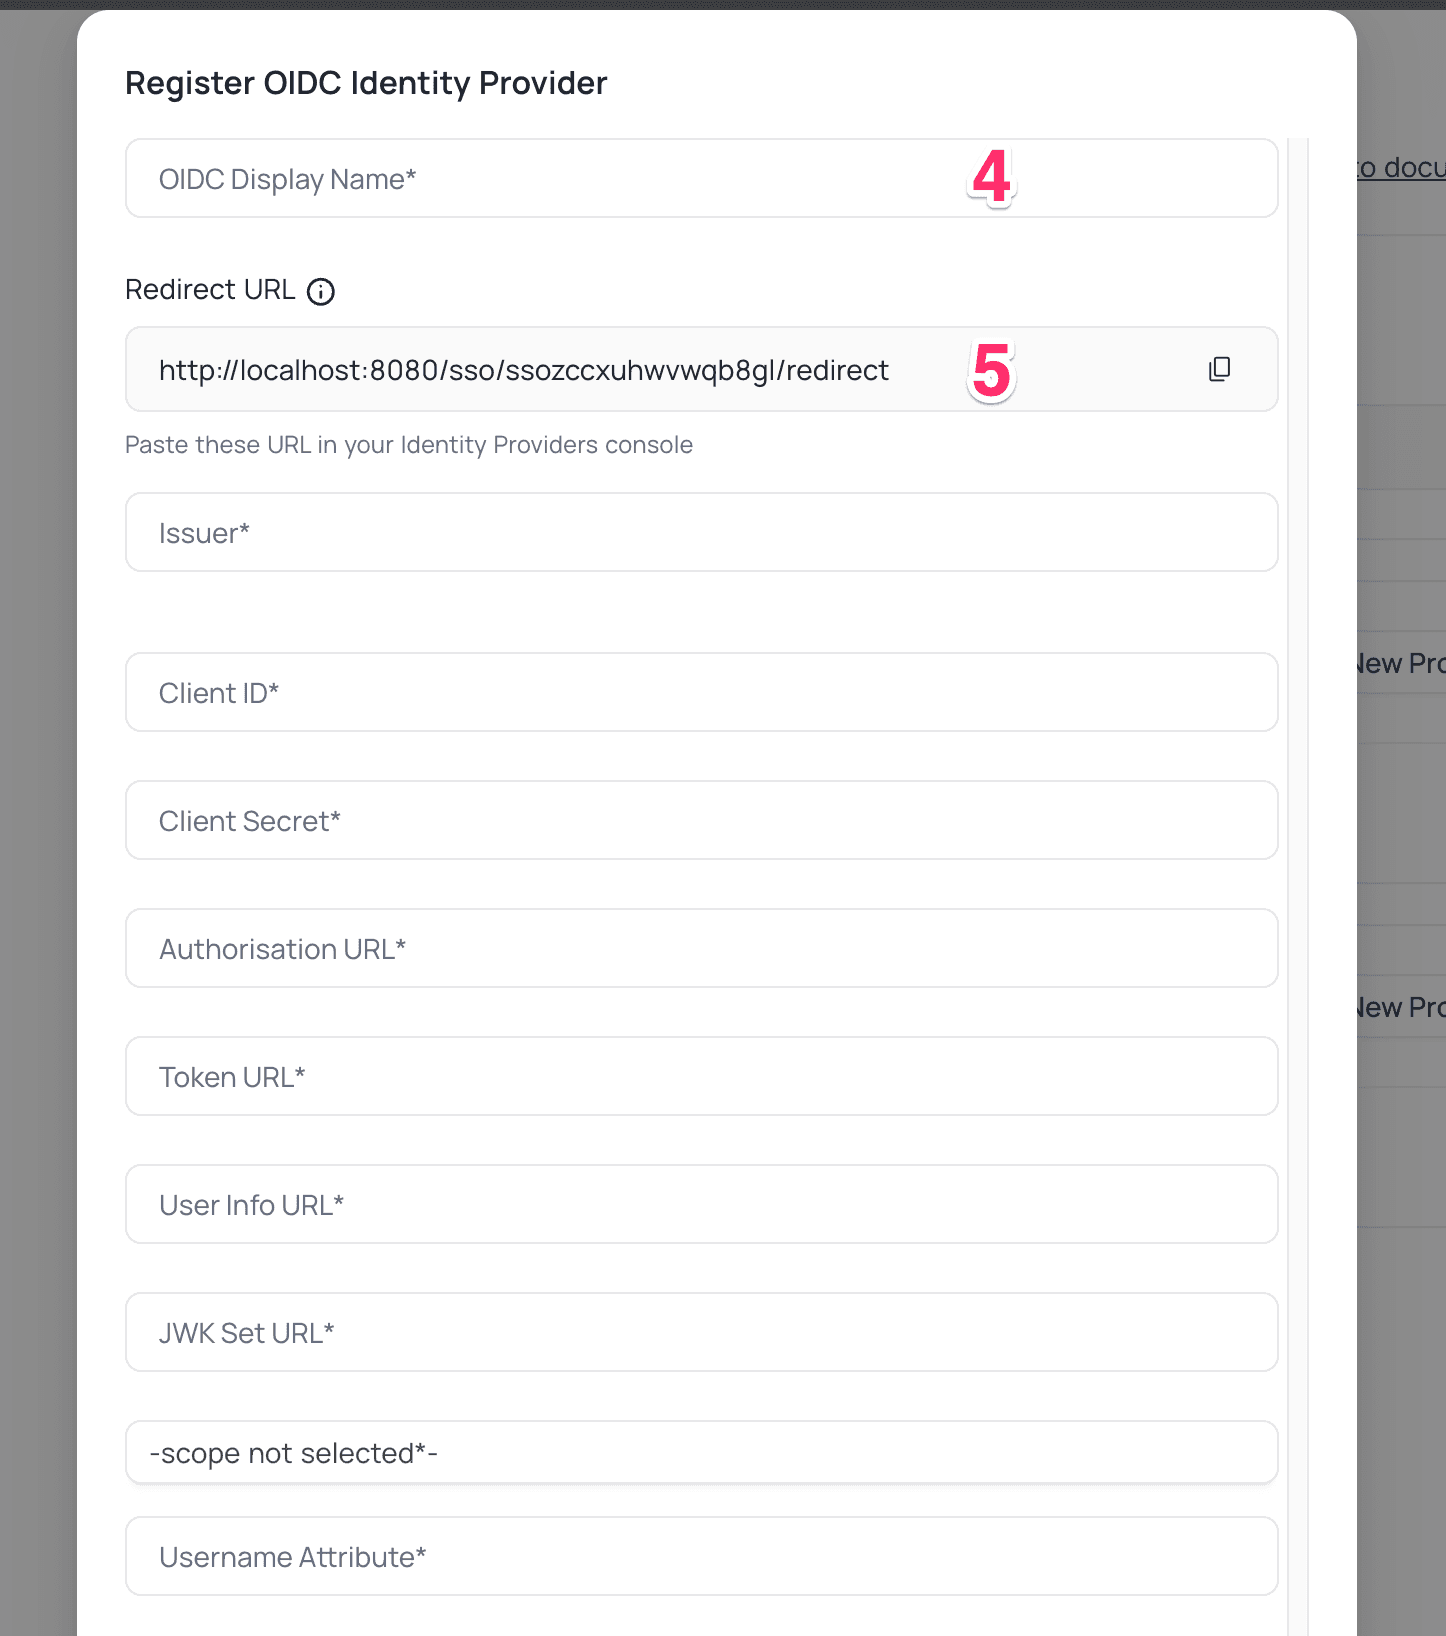
Azure AD, Configure NocoDB as an Application
- Sign in to your Azure account. Below
Azure Services, go toAzure Active Directory. - In the navigation bar, open
Manage Tenants. Select your directory, and clickSwitch. - On the homepage of your directory, in the navigation bar, click
+ Add>App Registration. - On the
Register an applicationpage:- Type the name of your application.
- Set the
Supported account typestoAccounts in this organizational directory only. - Select
Webas the Application type. - Below
Redirect URIs, add theRedirect URL. - Click
Register.
- On the homepage of your application:
- Copy the
Application (client) ID. - In the
Client credentialssection, clickAdd a certificate or secret. - On the
Certificates & secretspage, go to theClient secretssection. - Click
New client secret. - On the
Add a client secretpage:- Add a description for the secret.
- Set the expiration that you need.
- Click
Add.
- Copy the
Valueof the new secret.
- Copy the
- On the homepage of your application:
- Go to the
Endpointstab. - Open the
OpenID Connect metadata documentURL. From the JSON response, copyauthorization_endpoint,token_endpoint,userinfo_endpointandjwks_uri.
- Go to the
- Configure the scopes:
- Go to the
API permissionstab. - Click
Add a permission. - On the
Request API permissionspage:- From
Microsoft APIs, selectMicrosoft Graph. - Select
Delegated permissions. - From the
Select permissionsdropdown, selectopenidprofileemailoffline_access. - From the
Usersdropdown, selectUser.Read. - Click
Add permissions.
- From
- On the
API permissionspage, clickGrant admin consent for this directory.
- Go to the
NocoDB, Configure Azure AD as an Identity Provider
In NocoDB, open Account Settings > Authentication > OIDC. The "Register OIDC Identity Provider" modal opens. Enter this information:
| NocoDB field | Value |
|---|---|
Client ID | The Application (client) ID from step (7) above |
Client Secret | The Value of the new secret from step (7) above |
Authorization URL | The authorization_endpoint from step (8) above |
Token URL | The token_endpoint from step (8) above |
Userinfo URL | The userinfo_endpoint from step (8) above |
JWK Set URL | The jwks_uri from step (8) above |
Scope | openid profile email offline_access |
The sign-in page now shows the Sign in with <SSO> option to users.
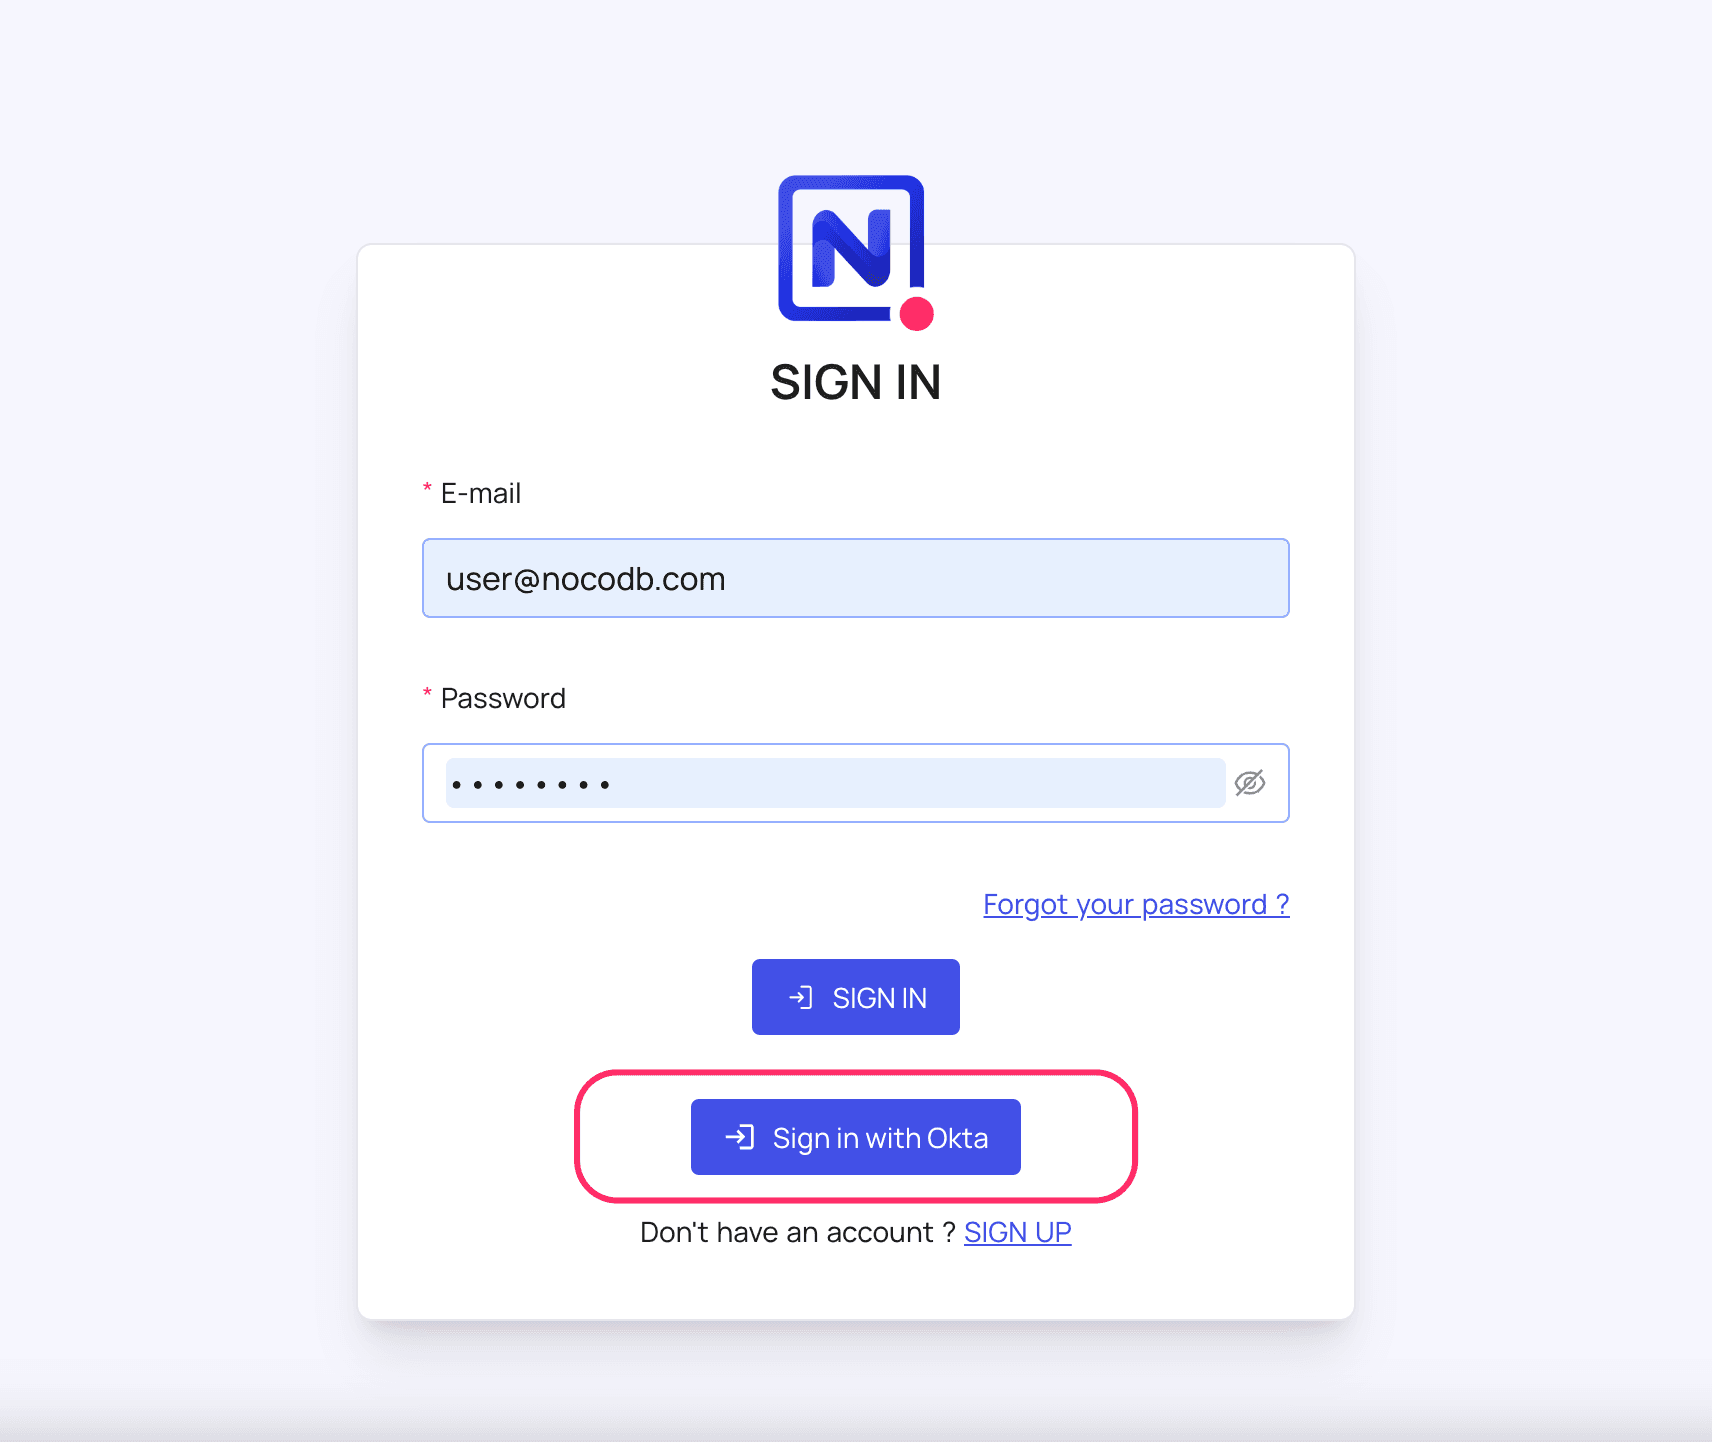
Post sign-out, refresh page (for the first time) if you do not see Sign in with SSO option
For more common questions and troubleshooting, see our SSO FAQ.
For information about Azure AD API Scopes, refer here.
Availability
- OIDC SSO is available on NocoDB Cloud (Business plan and above) and on licensed self-hosted deployments (Business plan and above). For access, reach out to sales.
- For users on the Business plan, the SSO configuration menu is in the workspace sidebar, at Settings > Single Sign-On (SSO). For more information, refer here.
- Domain Verification Required for Cloud Plans: Before you configure OIDC SSO, you must verify your domain in NocoDB. This is necessary for both Business and Enterprise plans in the cloud. Only users with email addresses from verified domains can sign in through SSO. For more information, refer to Domain Verification.
Last updated on
Latest product updates?See Changelog