Azure AD (Entra)
This article gives the steps to configure Active Directory as the identity provider for NocoDB.
NocoDB, Retrieve SAML SSO Configuration details
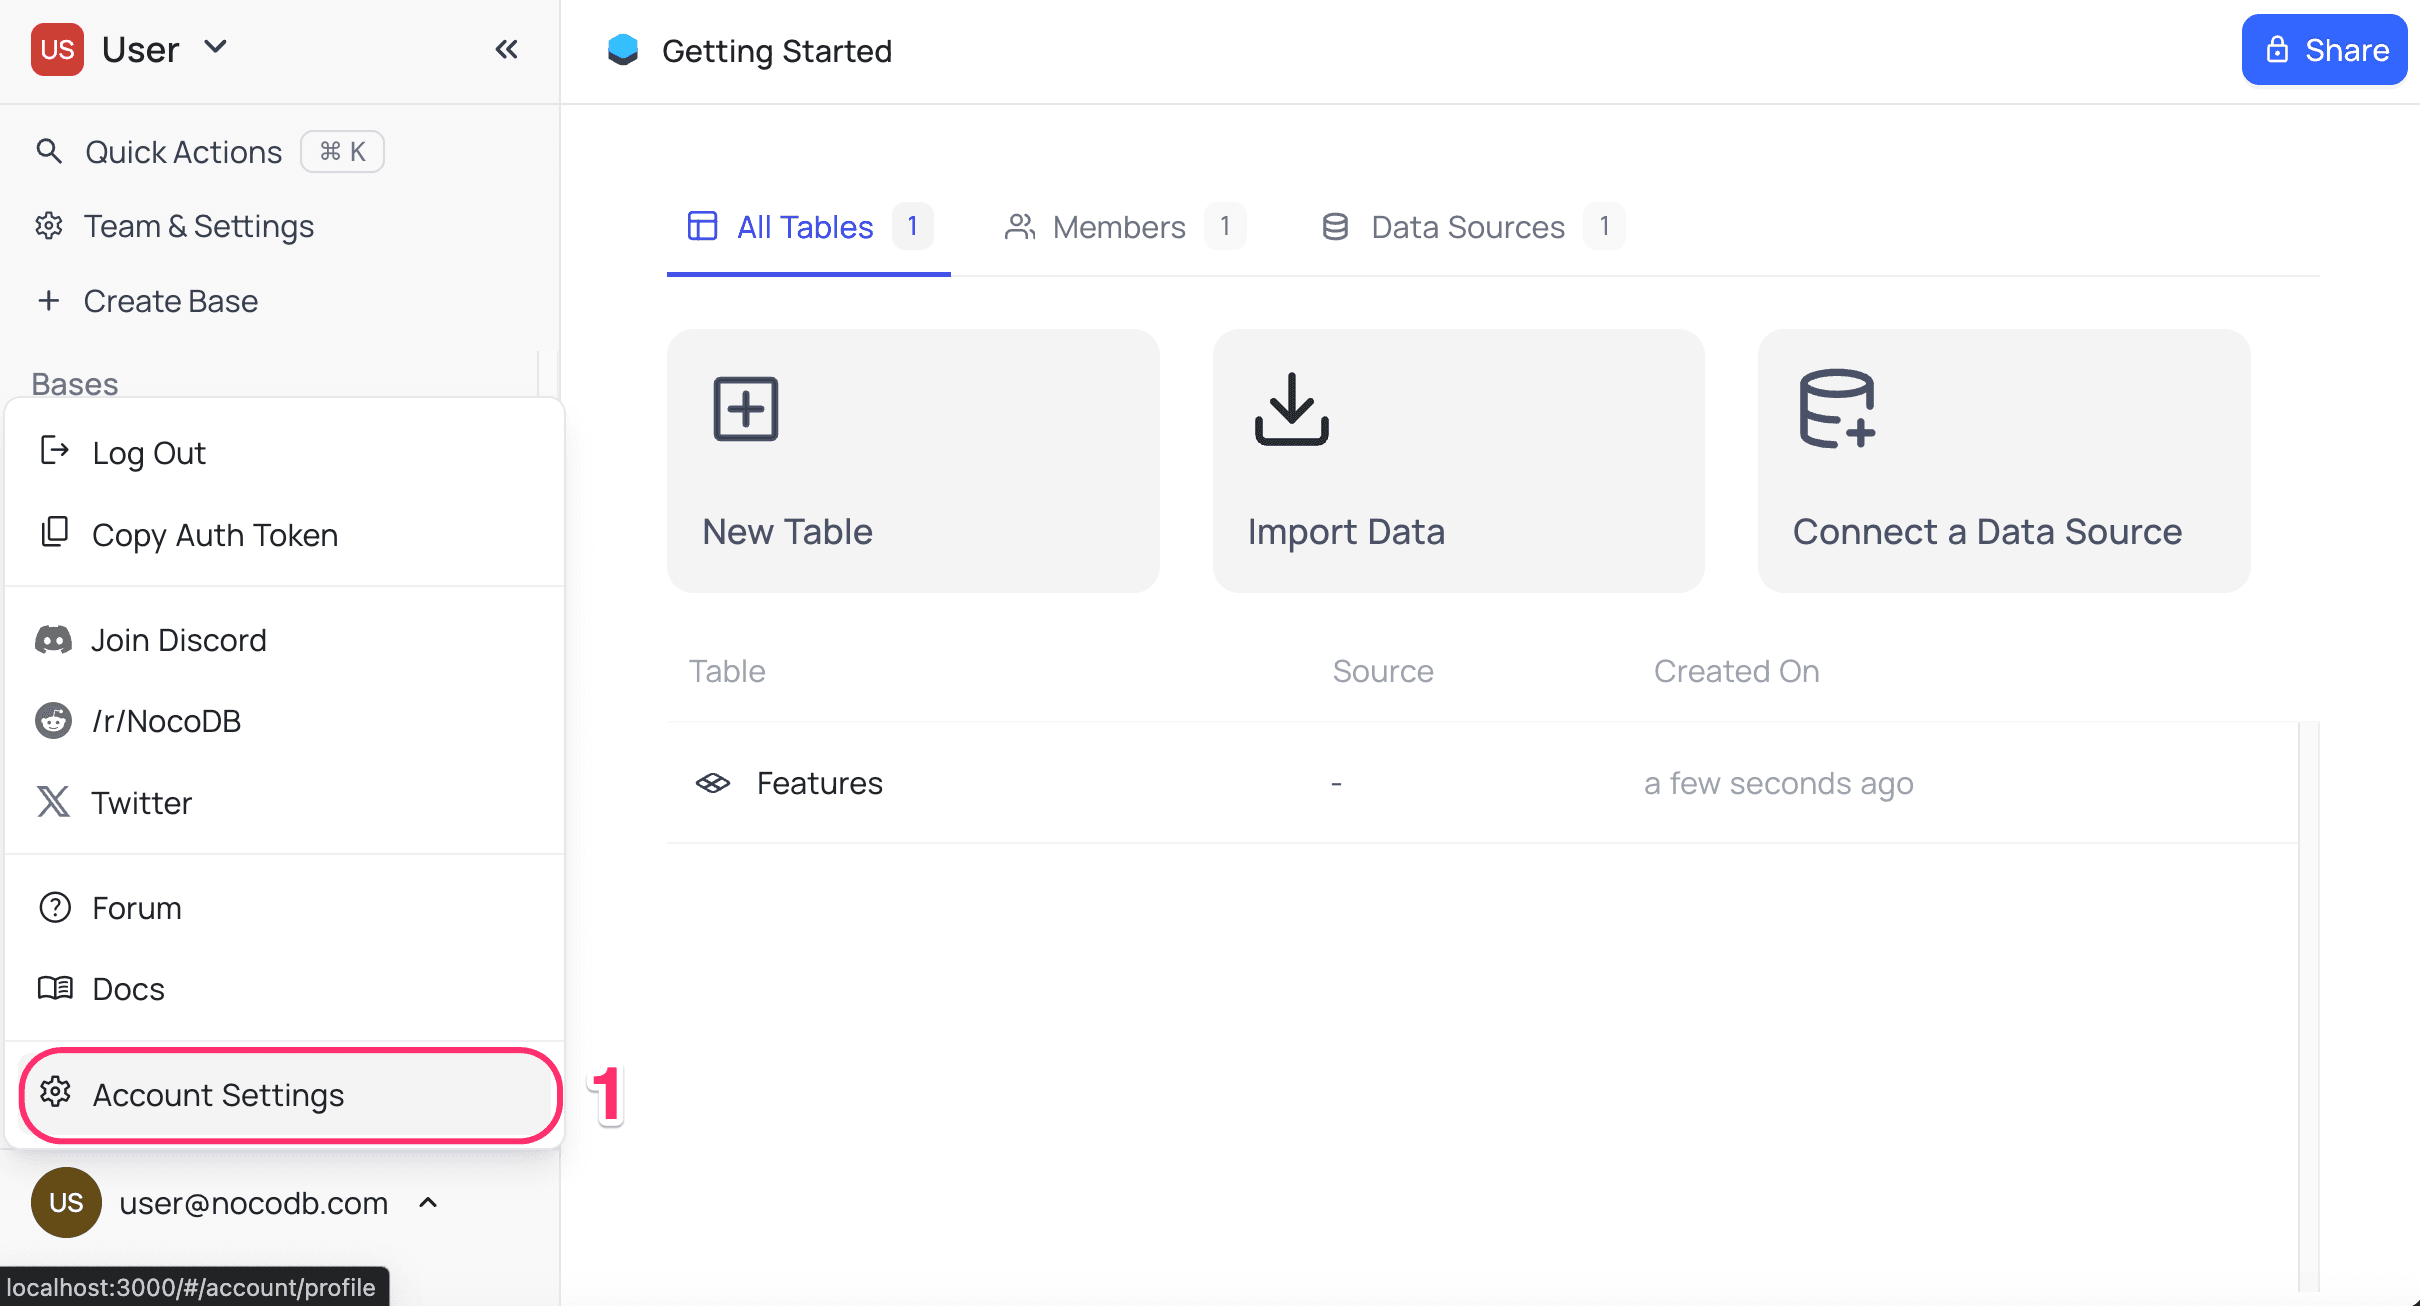
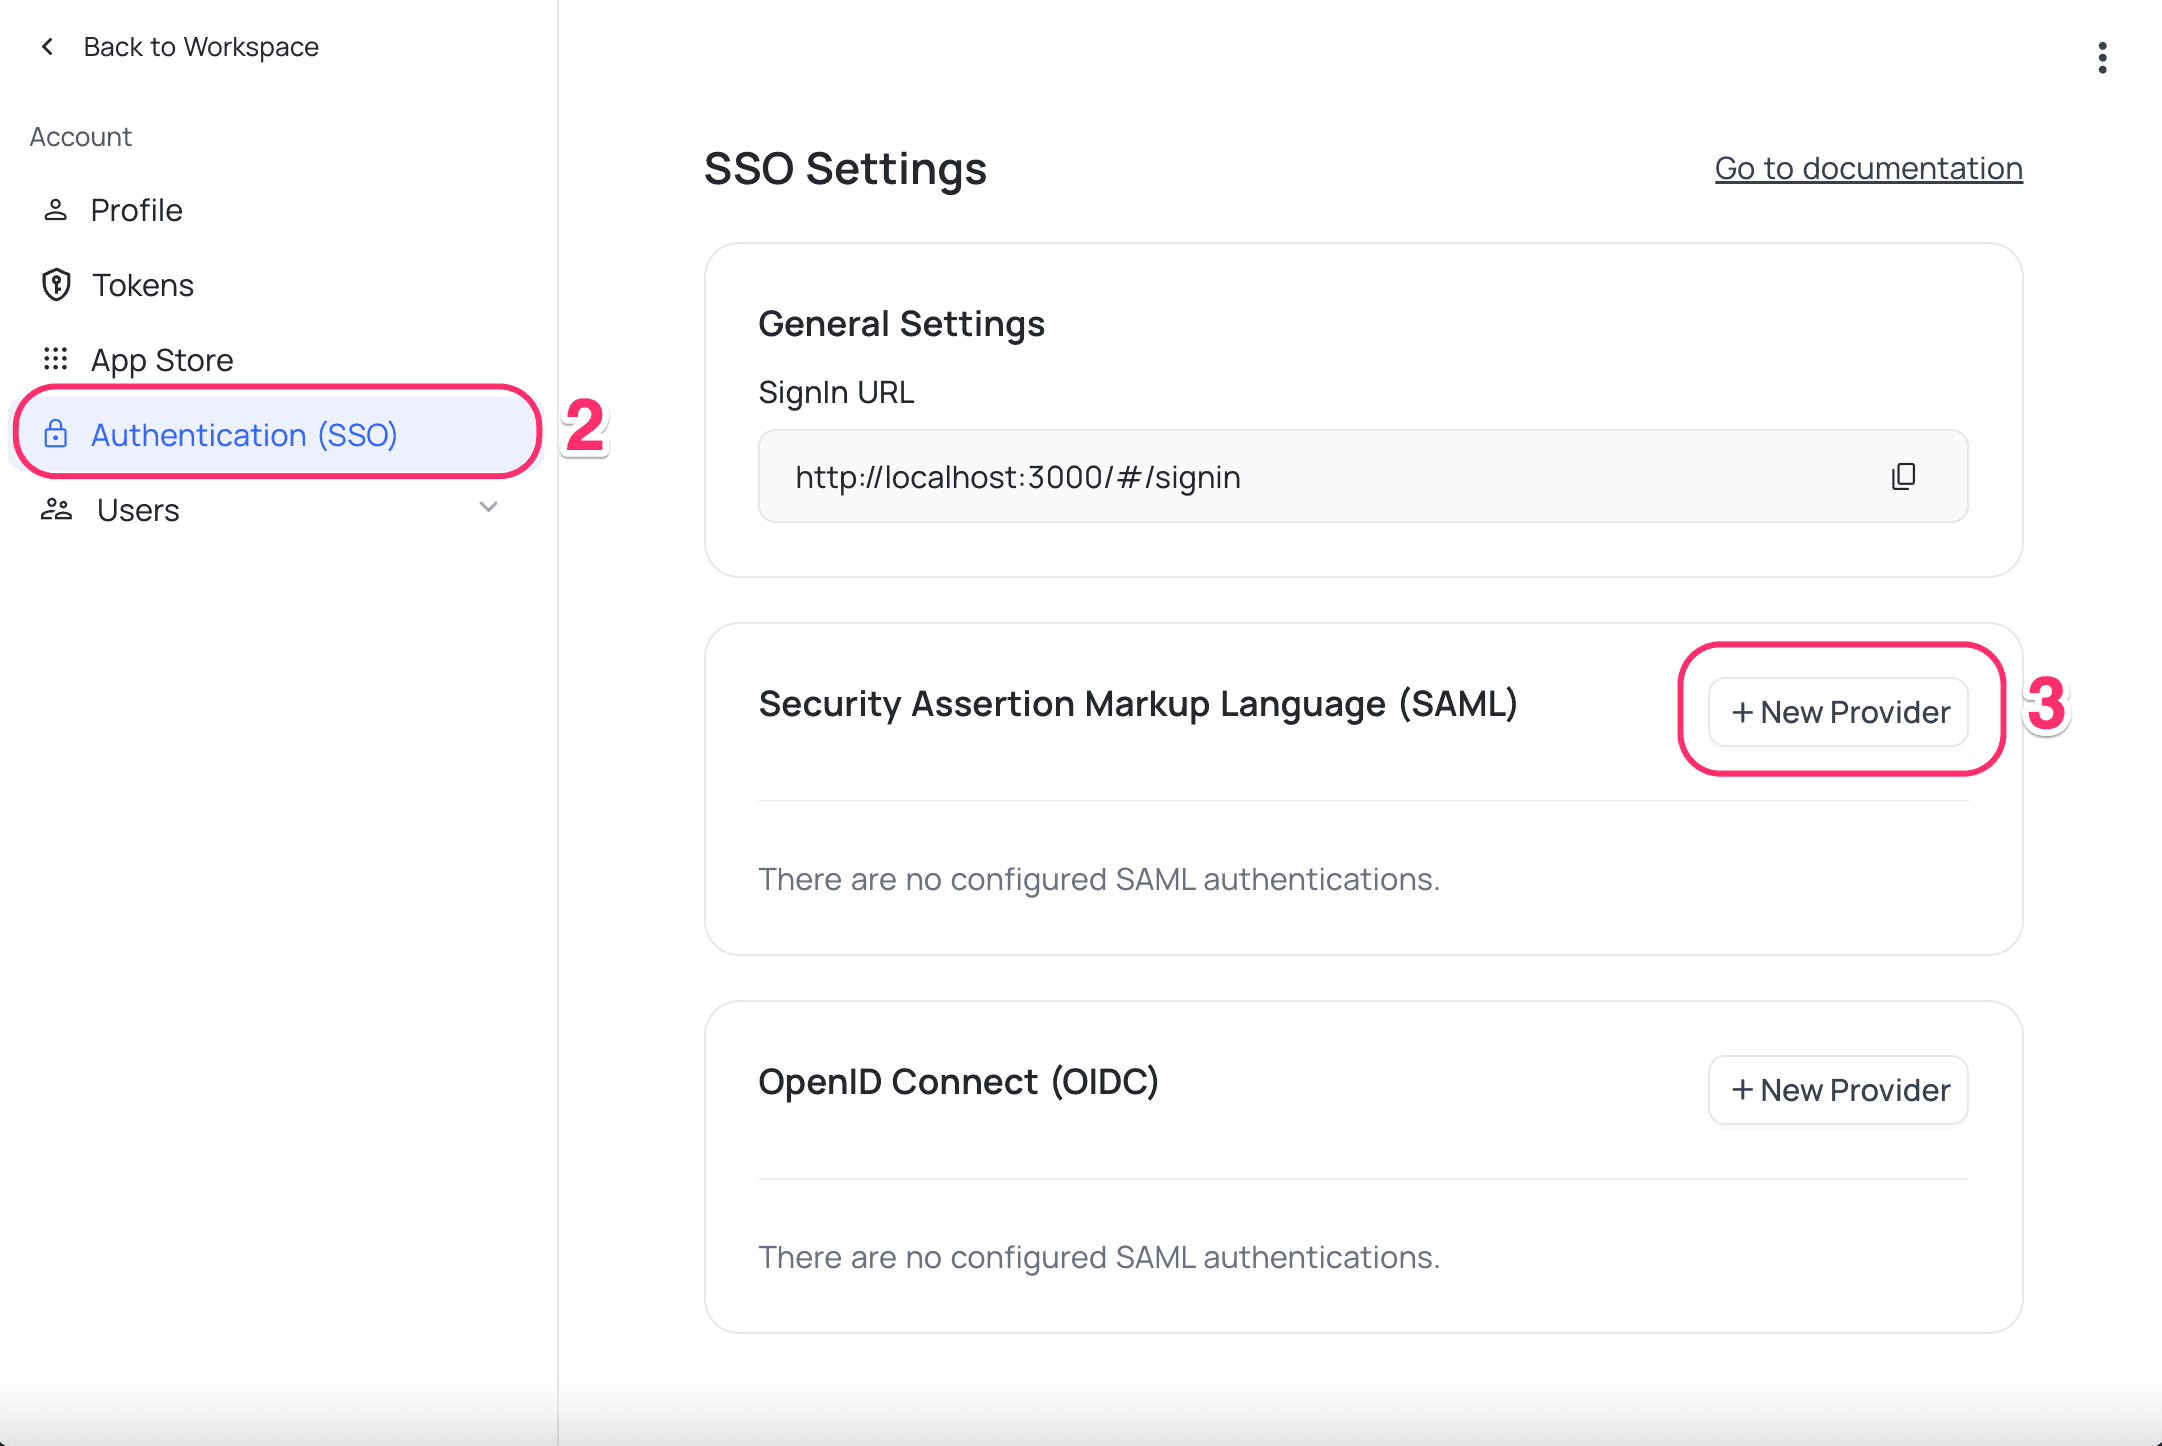
- Go to
Account Settings. - Select
Authentication (SSO). - Click the
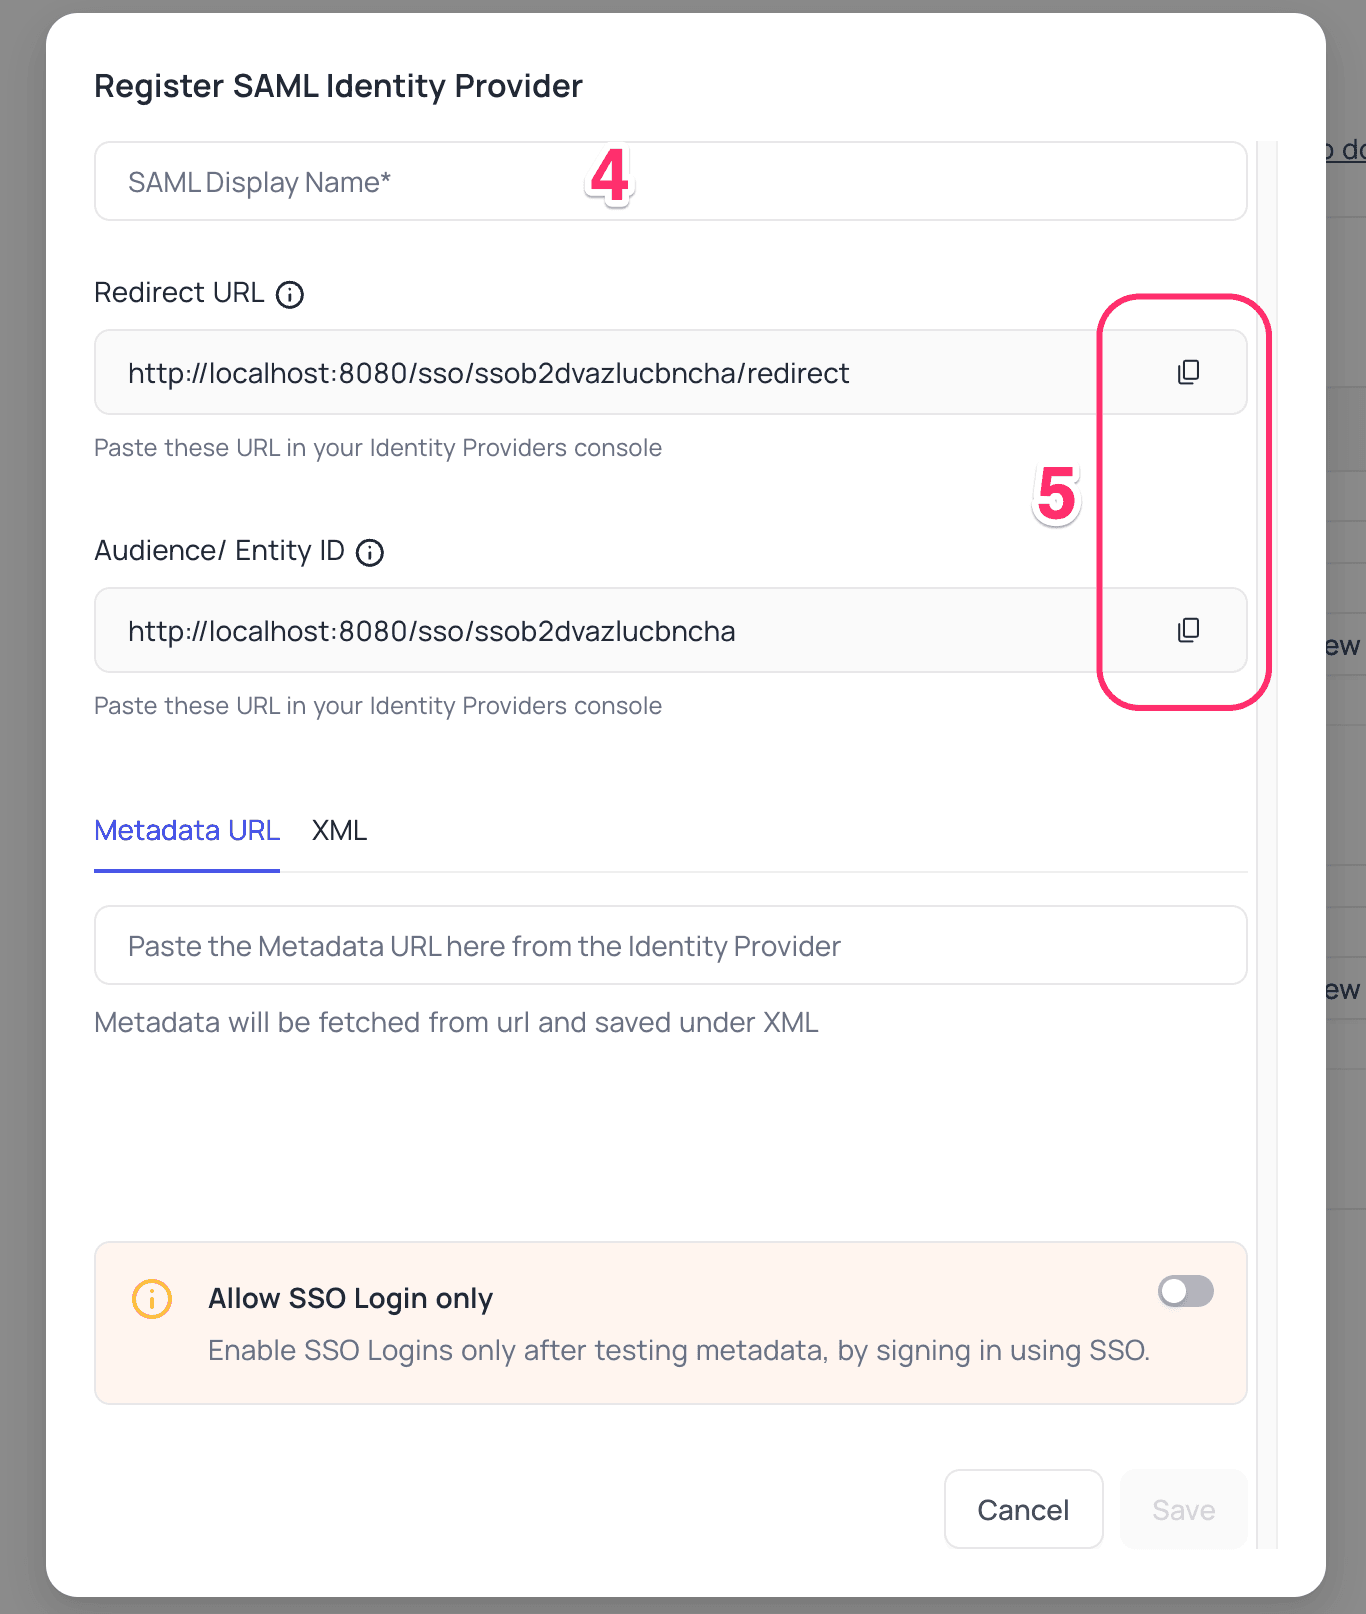
New Providerbutton. - In the dialog, type a
Display namefor the provider. The login page shows the provider with this name. - Copy the
Redirect URL&Audience / Entity ID. You need these values later to configure the identity provider.
Azure AD, Configure NocoDB as an Application
- Sign in to your Azure account. Go to
Microsoft Entra admin center>Identity>Enterprise applications. - Click
+ New application. - On the
Browse Microsoft Entra Gallerypage, in the navigation bar, selectCreate your own application.- Type a name for your application.
- Select
Integrate any other application you don't find in the gallery (Non-gallery). - Click
Create.
- On your application page, go to
Manage>Single sign-on>SAML. - Below
Set up Single Sign-On with SAML, go to theBasic SAML Configurationsection and clickEdit.- Below
Identifier (Entity ID), add theAudience URI. - Below
Replay URL (Assertion Consumer Service URL), add theRedirect URL. - Click
Save.
- Below
- In the
Attributes & Claimssection, clickEdit.- Edit the "Unique User Identifier (Name ID)" claim:
- From the
Name identifier formatdropdown, selectEmail address. - For the
Source, selectAttribute. - In the
Source attribute, selectuser.mail. - Click
Save.
- From the
- Edit the "Unique User Identifier (Name ID)" claim:
- Go to the
SAML Certificatessection. Copy theApp Federation Metadata URL. - On the application's Overview page:
- Click
Users and groups. - Add the users or groups that need access to the application.
- Click
NocoDB, Configure Azure AD as an Identity Provider
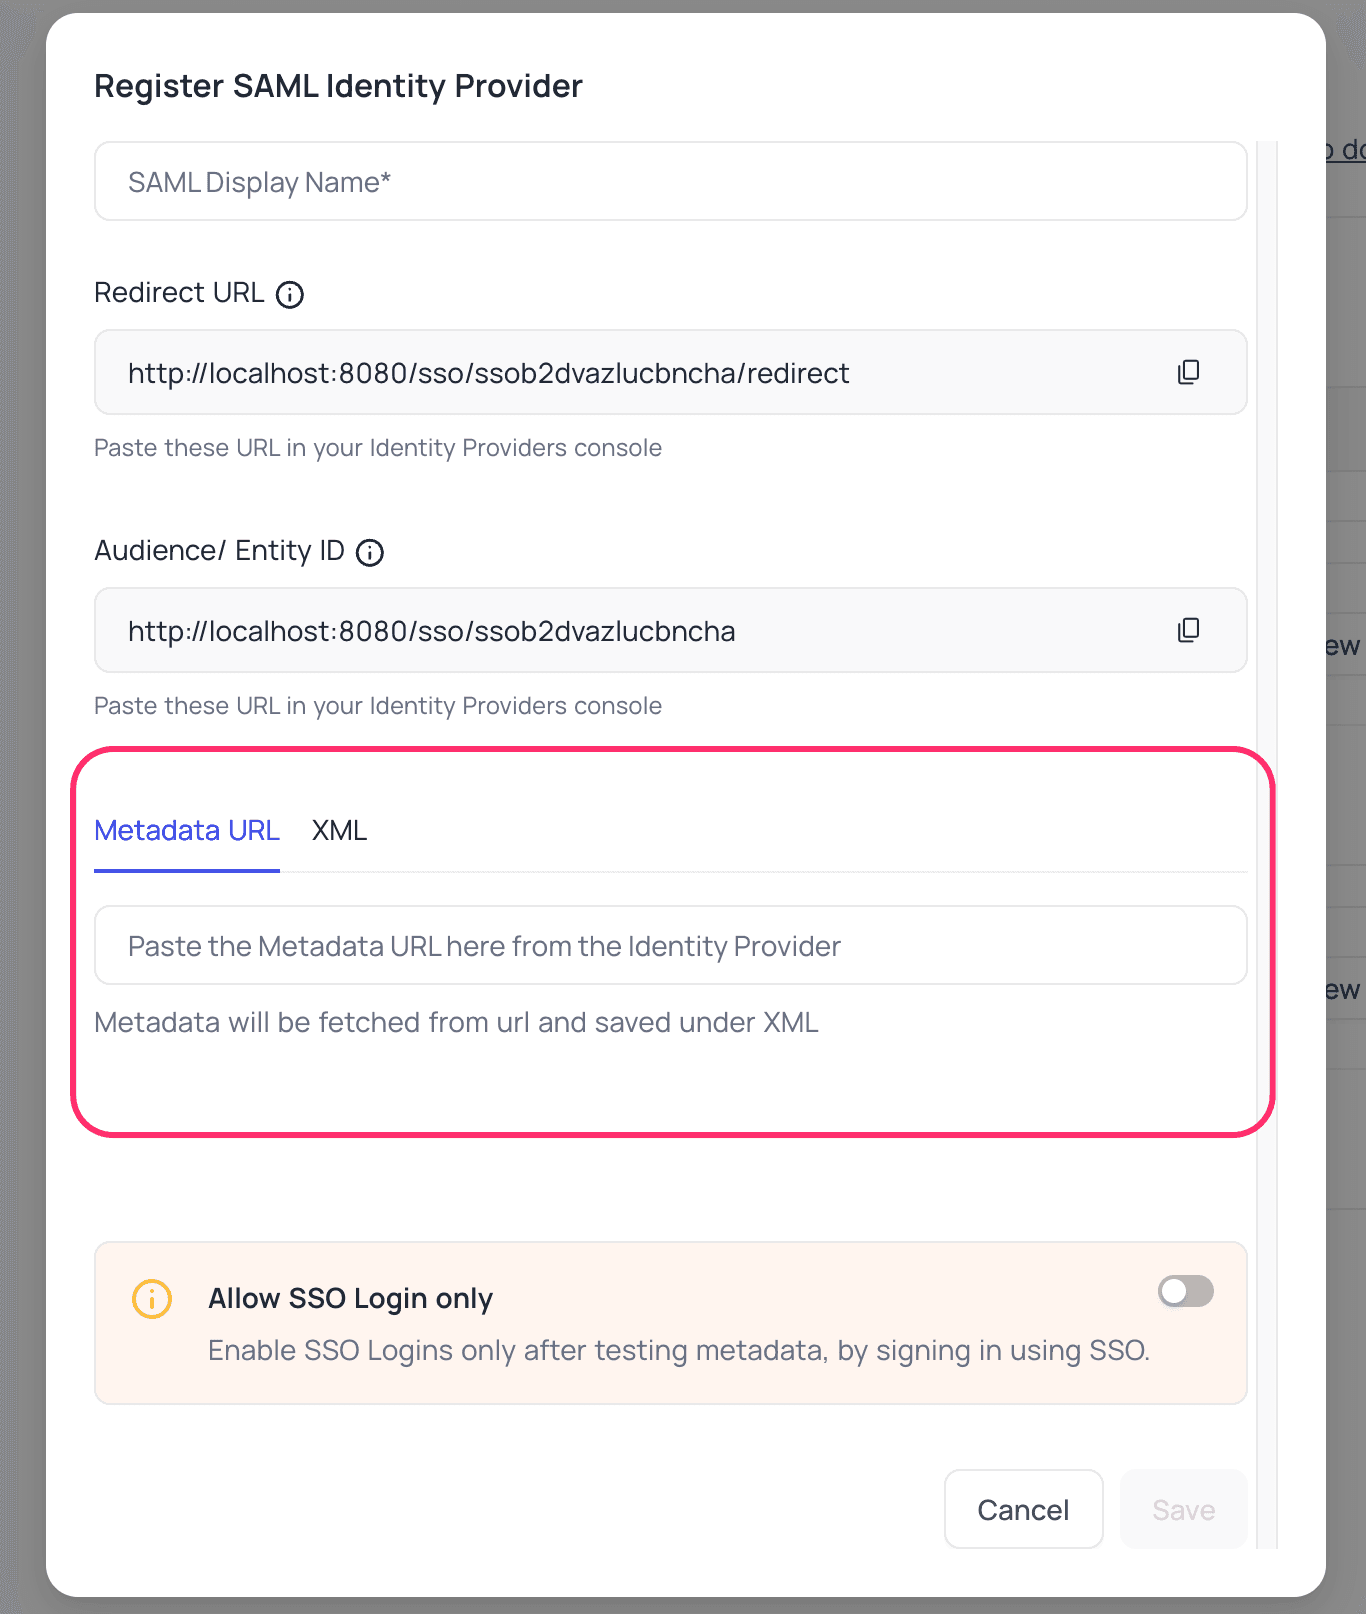
- Go to
Account Settings>Authentication>SAML. - Enter the
Metadata URLfrom the step above. You can also configure the XML directly. - Click
Save.
Users now see the Sign in with <SSO> option on the sign-in page.
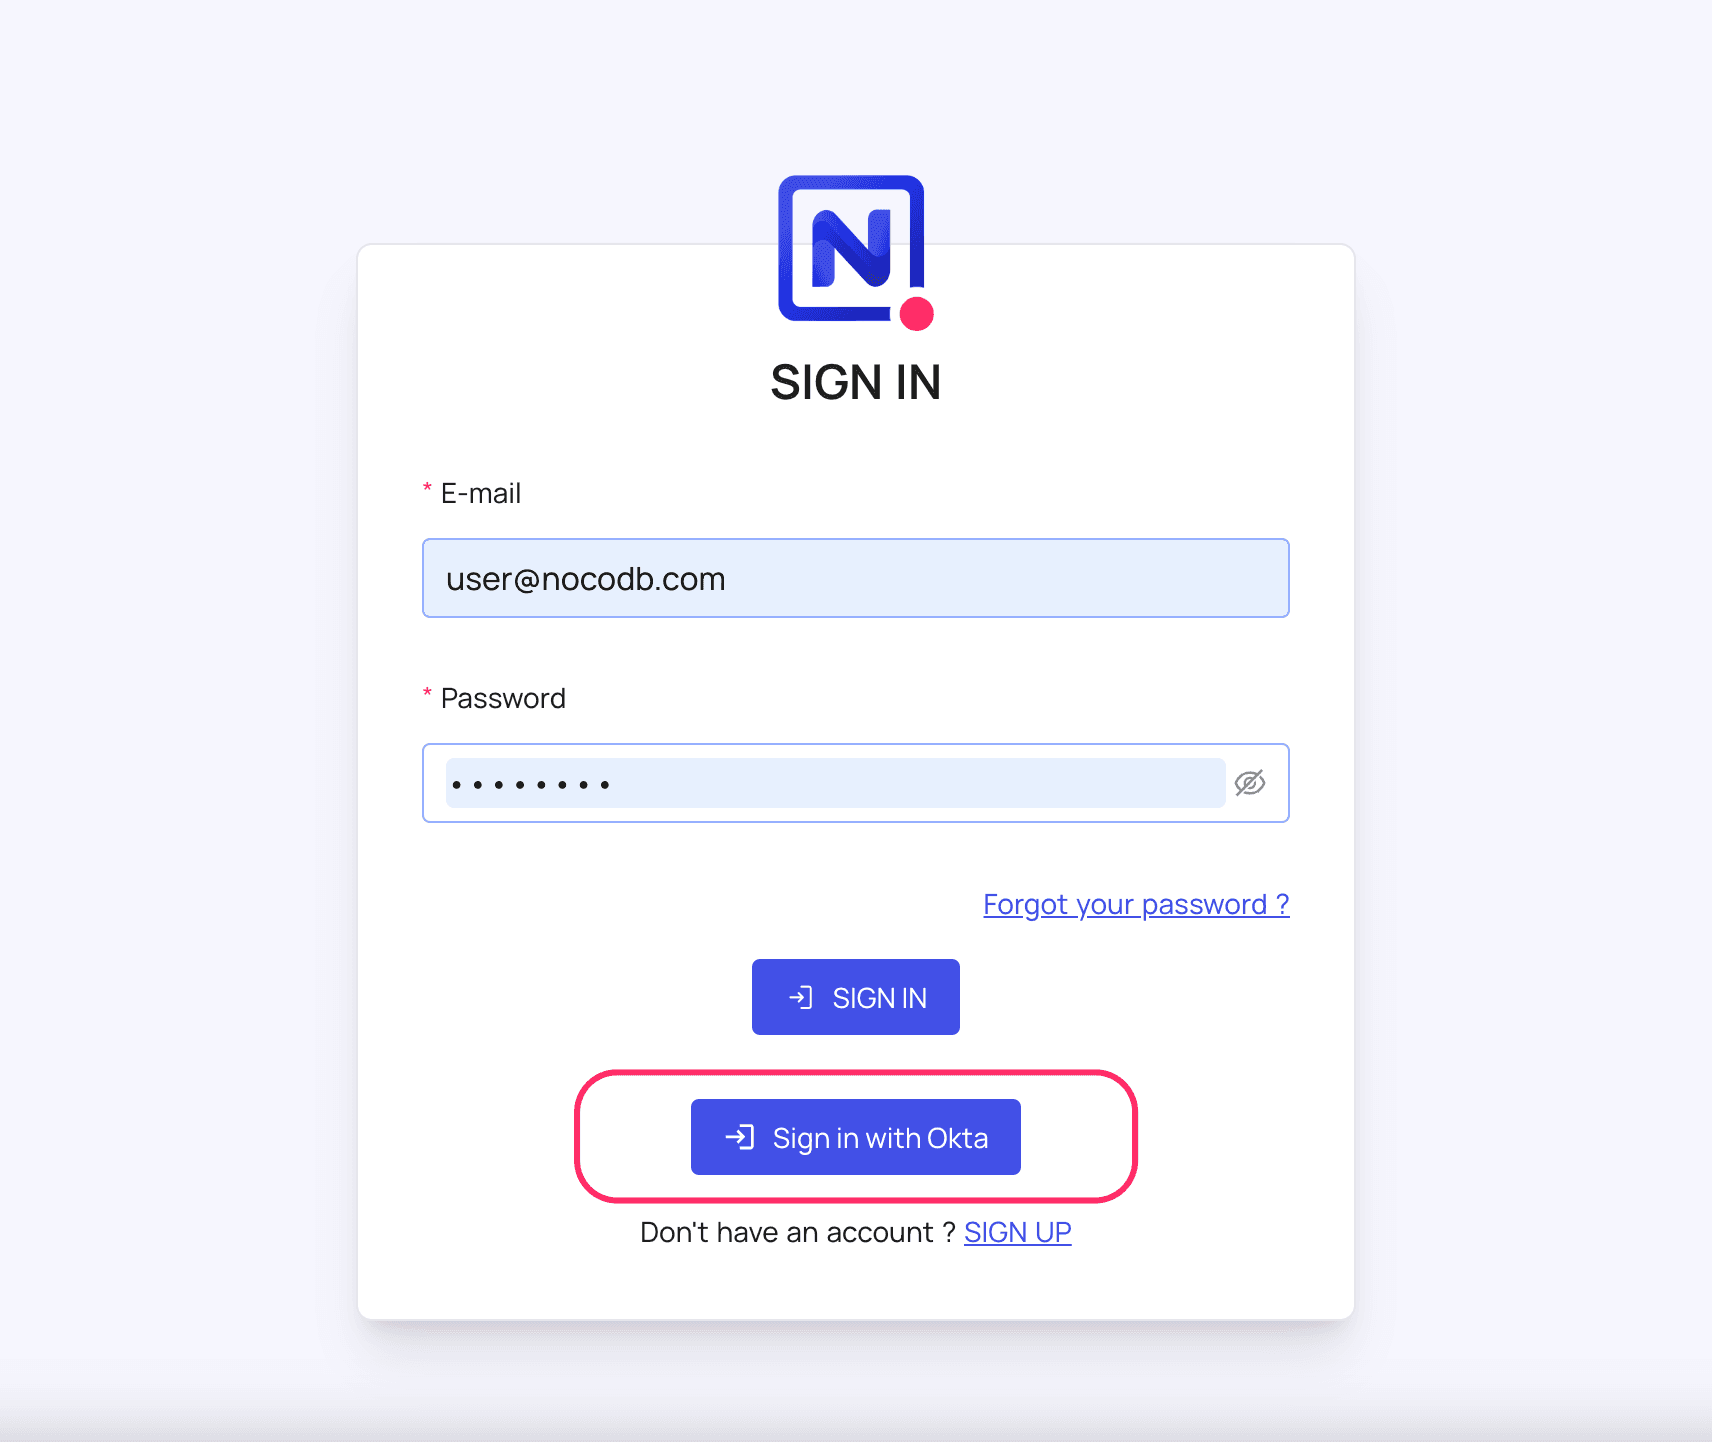
Post sign-out, refresh page (for the first time) if you do not see Sign in with SSO option
For more common questions and troubleshooting, see our SSO FAQ.
Availability
- SAML SSO is available on NocoDB Cloud (Business plan and above) and on licensed self-hosted deployments (Business plan and above). For access, reach out to sales team.
- On the Business plan, the SSO configuration menu is in the workspace sidebar, at Settings > Single Sign-On (SSO). For more details, refer here.
- Domain Verification Required for Cloud Plans: Verify your domain in NocoDB before you configure SAML SSO. Cloud Business and Enterprise plans both need this. Only users with email addresses from verified domains can sign in with SSO. For details, see Domain Verification.
Last updated on
Latest product updates?See Changelog